
offing
io.github.velella-sh/offing
Evidence-backed deprecation and end-of-life checks for dependencies, runtimes, and Actions.
Documentation

Offing
See what's in the offing. Fix it before it lands.
Local-first end-of-life and deprecation scanner for your repository.




Offing finds end-of-life and deprecated runtimes, packages, and GitHub Actions in your repository, at the exact file and line, each with an authoritative source, a replacement, and migration steps. It is deterministic, offline, and needs no account.
npx @velella/offing scan .
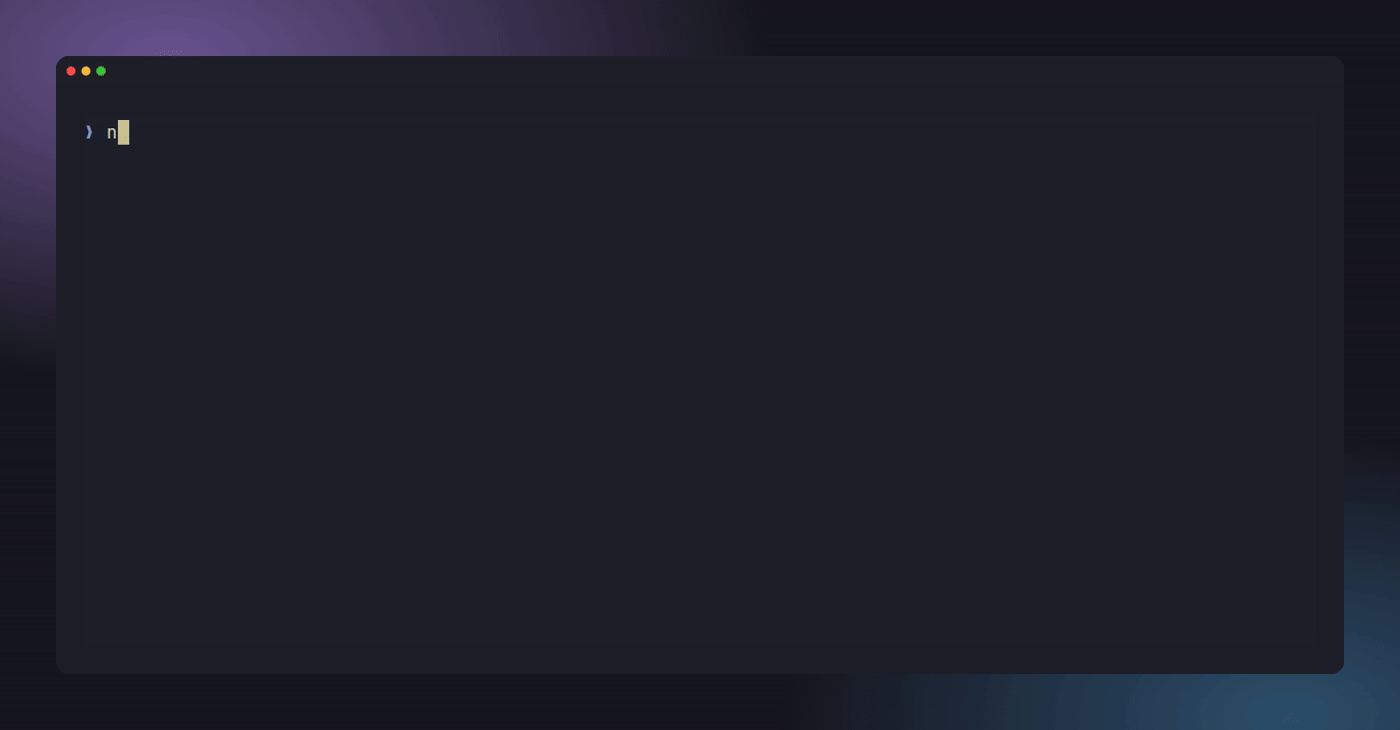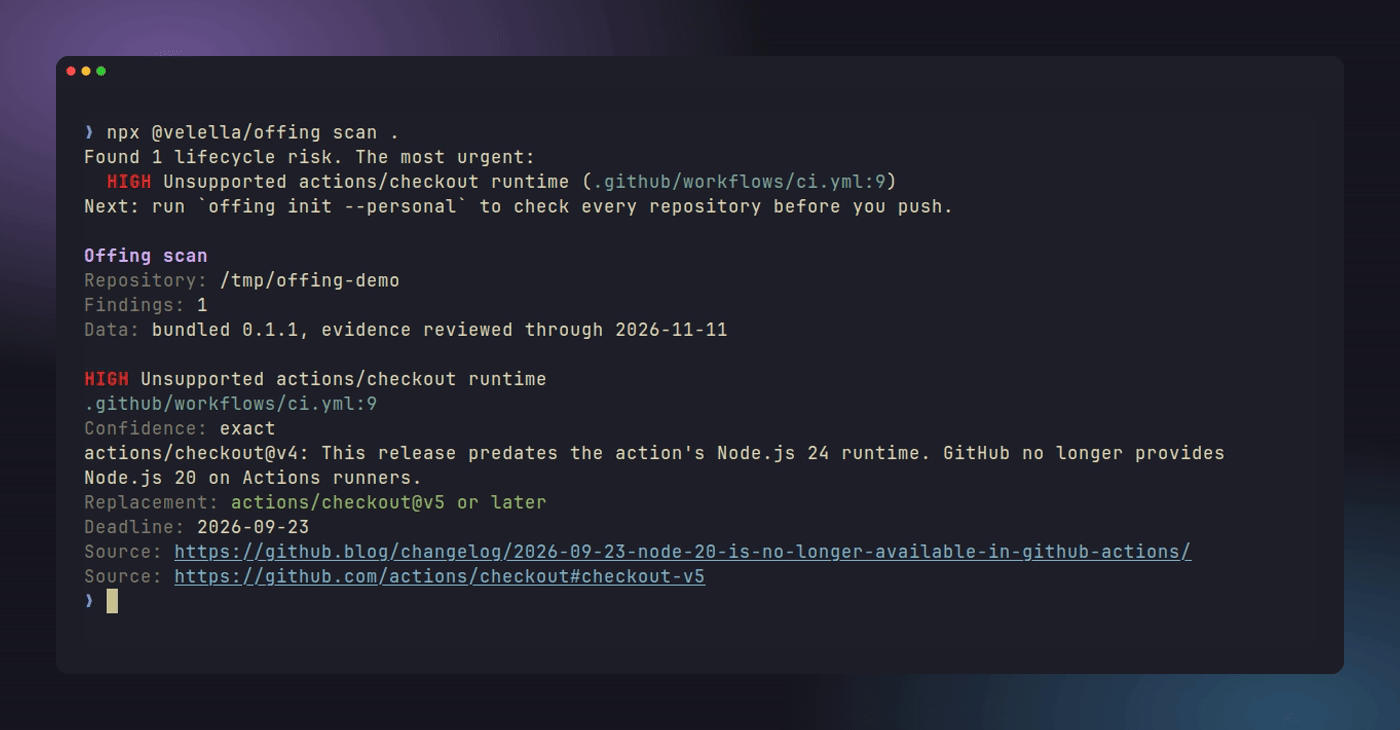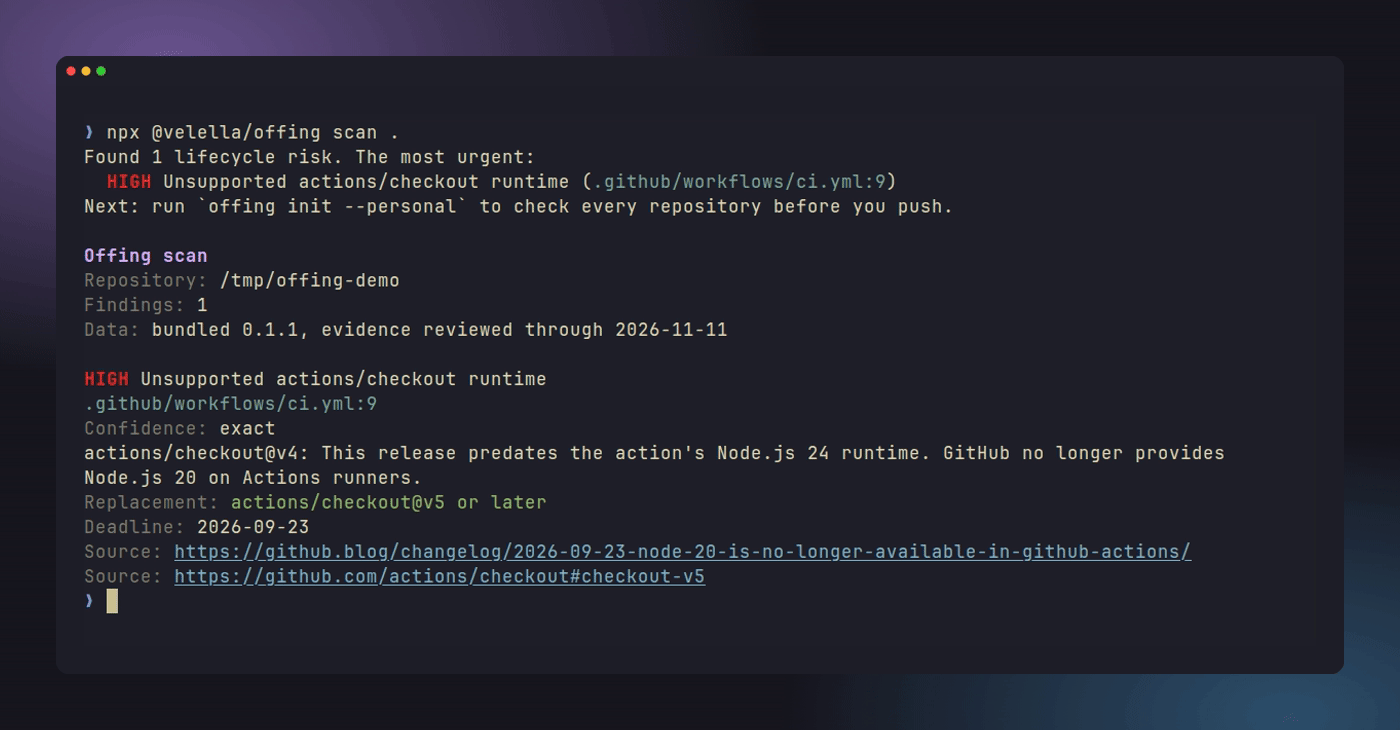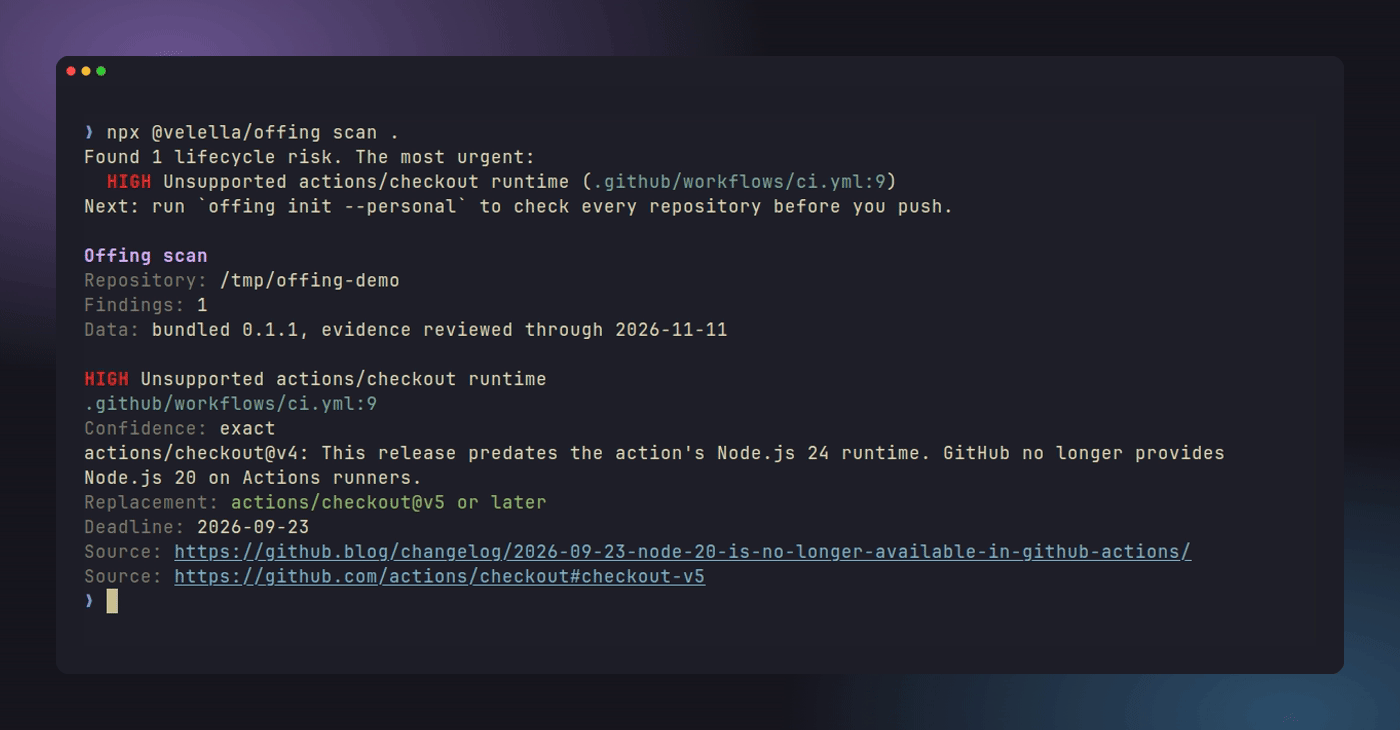
Offing: 1 finding
github-actions.checkout.node20:.github/workflows/ci.yml:9 .github/workflows/ci.yml:9 high actions/checkout@v5 or later
That is scan --format compact on the bundled demo project (examples/demo). Ask for the evidence behind one finding with npx @velella/offing explain '<finding-id>' ., or check a dependency before you add it:
npx @velella/offing check pkg:npm/request@2.88.2 # exits 1: deprecated, with the replacement and its source
Requirements: Node.js 22 or newer. Read this in: English · فارسی.
What you get
- Exact location, real source. Every finding names the file and line, links the authoritative source for the rule, and gives the replacement and migration steps. Nothing is guessed: a package with no rule reports
no-data, never "safe". - Check before you add.
check pkg:npm/request@2.88.2answers for one dependency without scanning anything, and exits1when a rule at or above--fail-onapplies. - Only new problems.
baselinerecords accepted findings;scan --baselinethen reports only regressions, so a legacy repository can adopt Offing on day one. - Migration packets.
context '<finding-id>' --jsonhands a person or a coding agent the constraints, the affected files and usages, the sources, and suggested verification commands. Offing never runs them for you. - Usage, not just declarations. For npm and Ruby it finds the imports and calls that use a deprecated package, so you see what a migration has to touch.
- Fresh data, still offline. Scans never touch the network.
data updaterefreshes lifecycle rules from signed bundles when you ask, and refuses anything it cannot verify. - Works where you work. CLI, local MCP server, GitHub Action with SARIF for code scanning, and an Agent Skill. Setup for Claude Code, Codex, Cursor, Gemini CLI, GitHub Copilot and Kilo Code is one command:
setup. - Private by design. No account needed, and no repository upload.
See it run
Check a dependency before you add it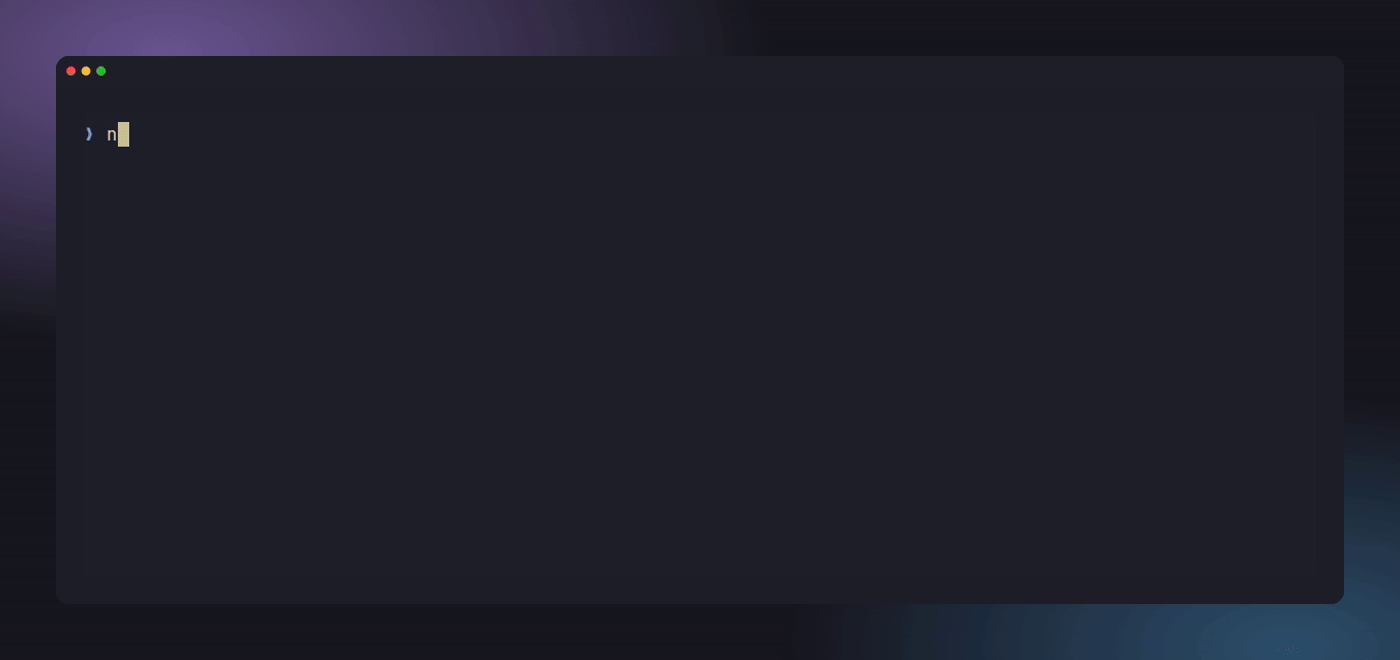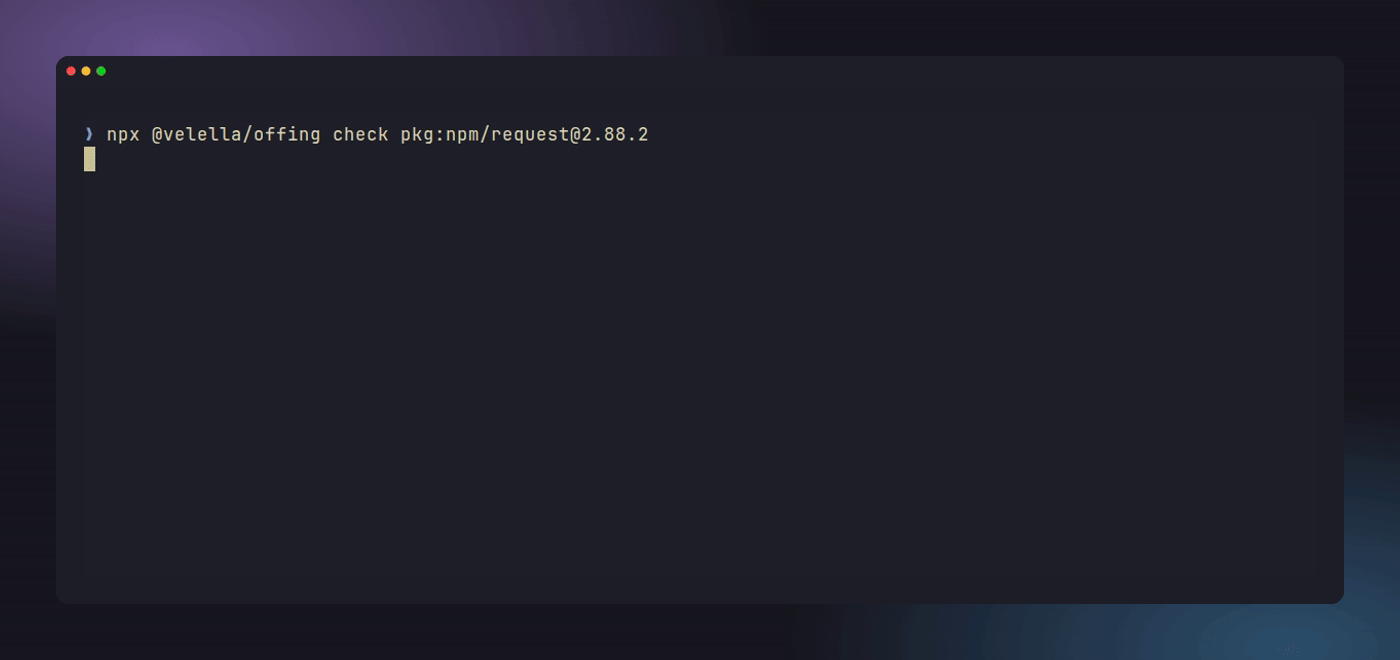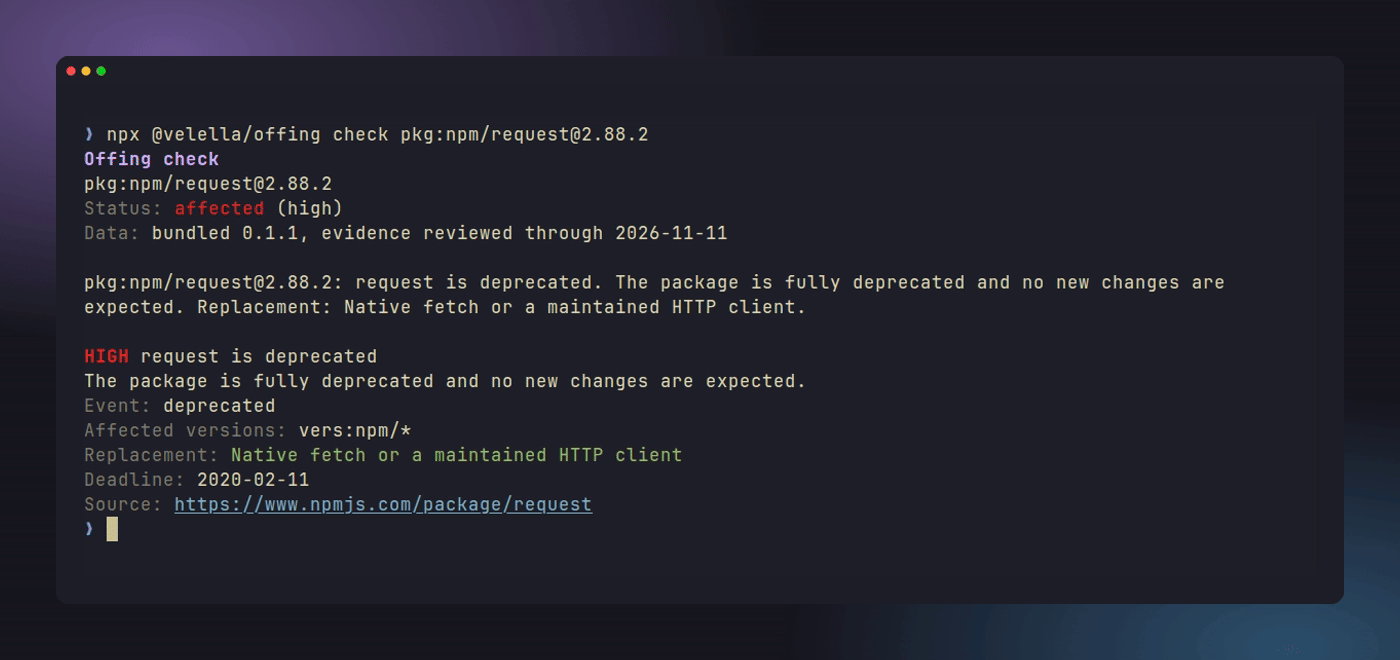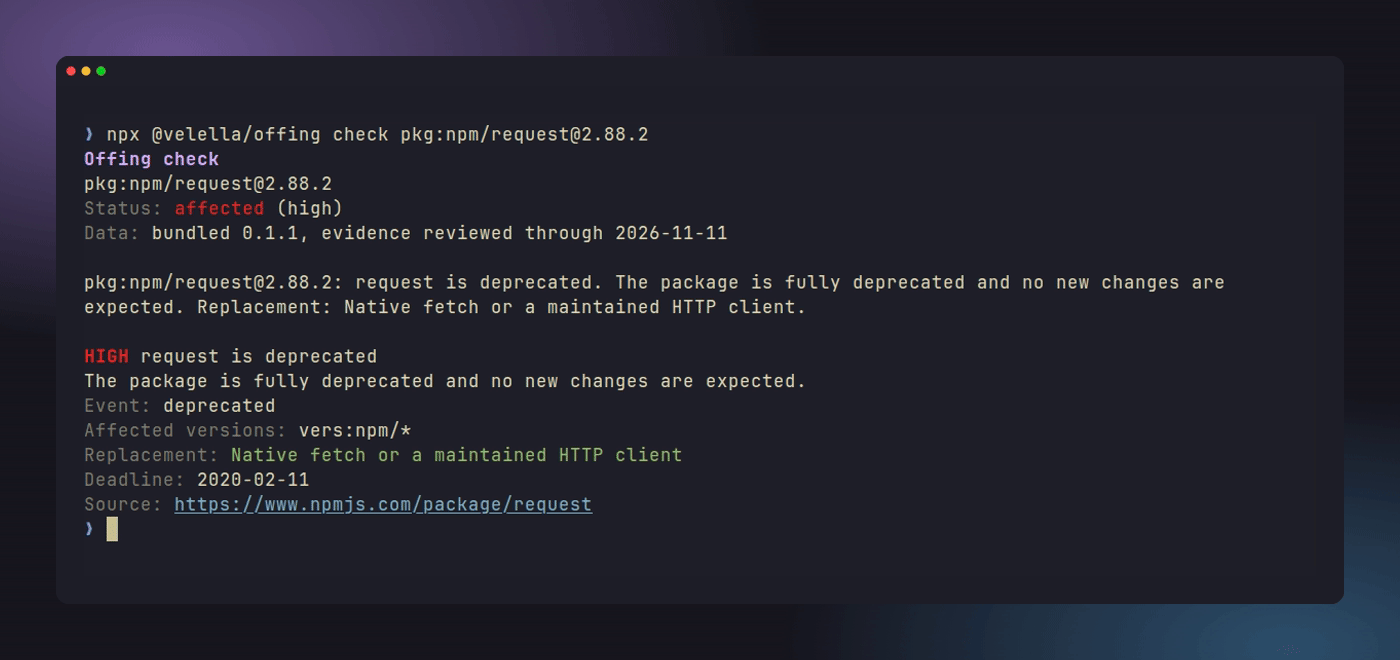 | Evidence behind one finding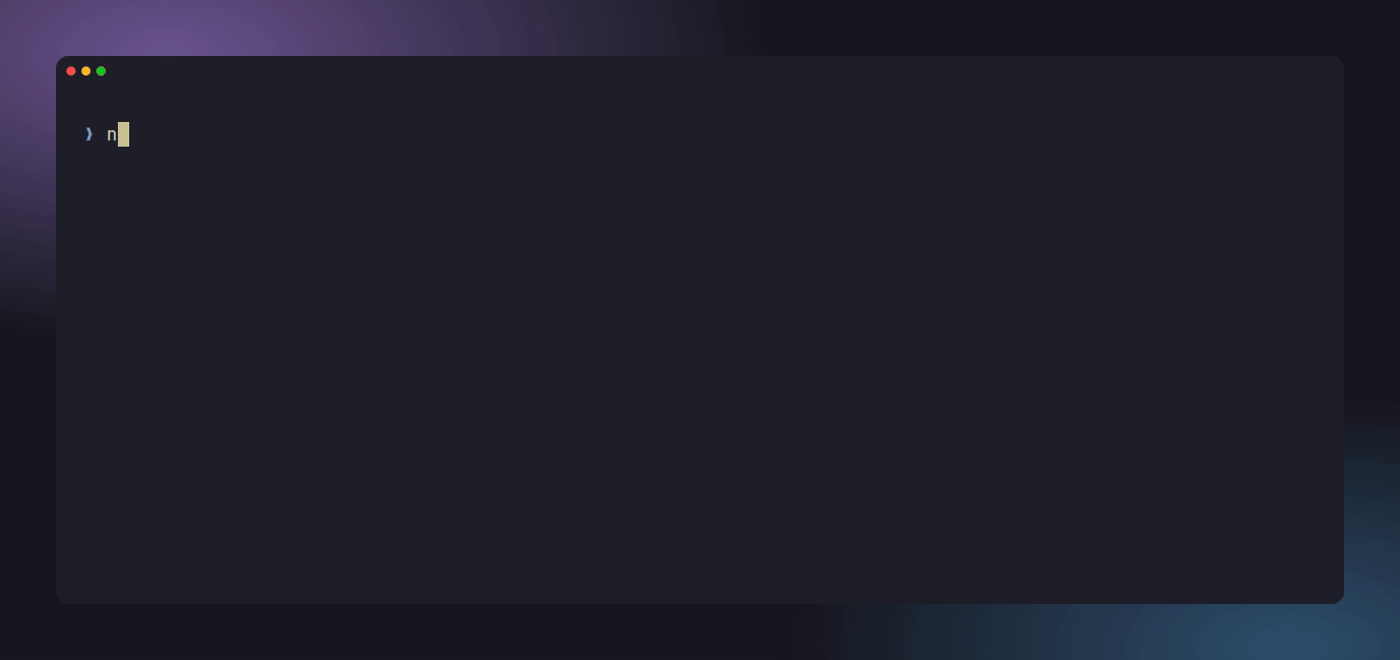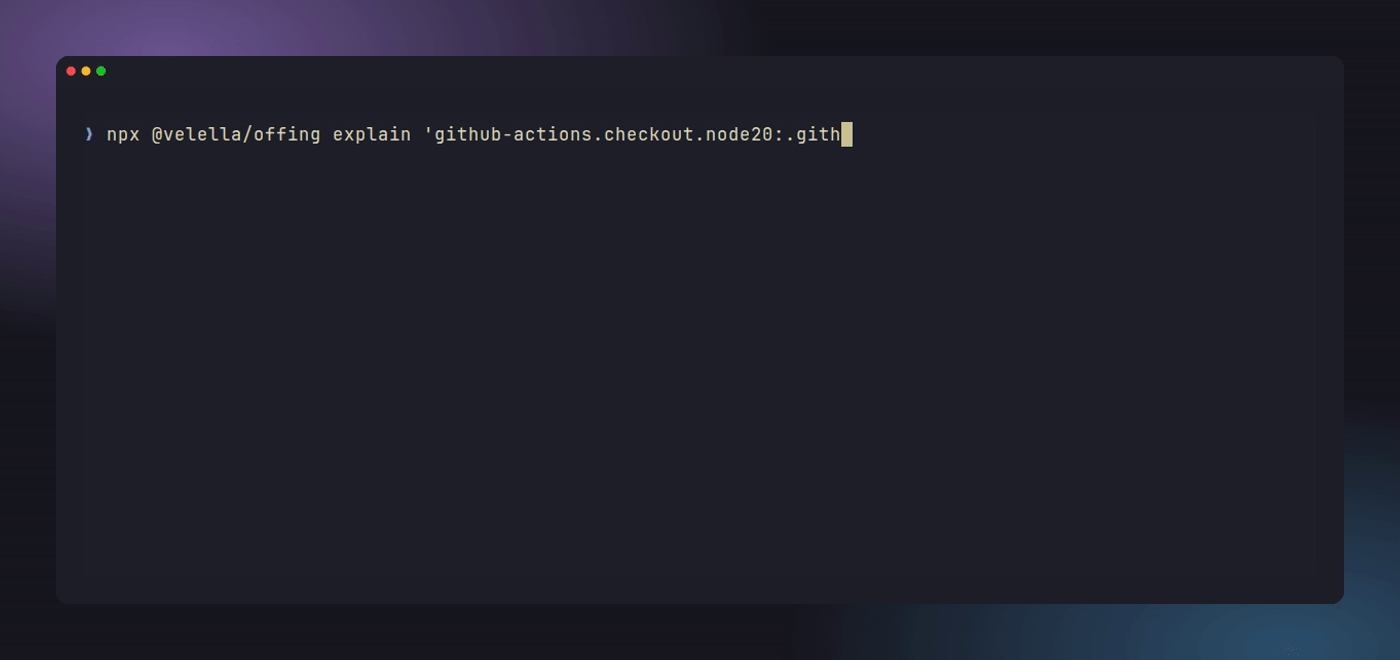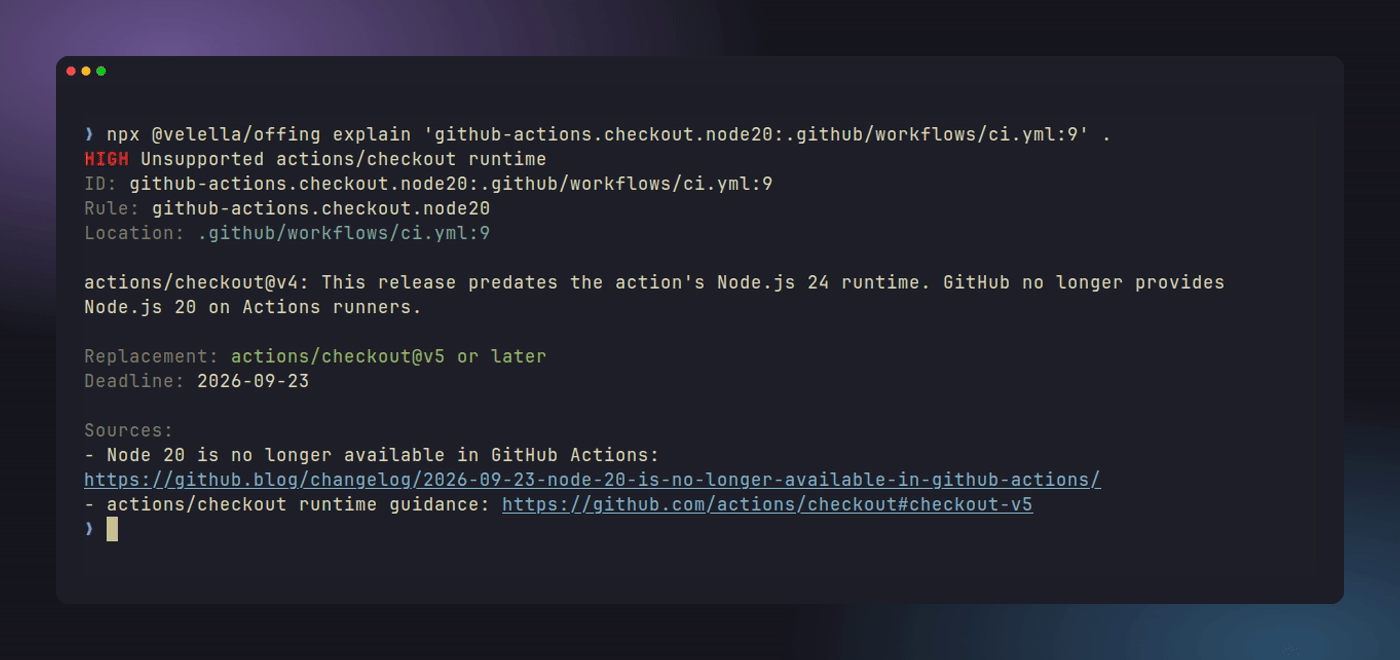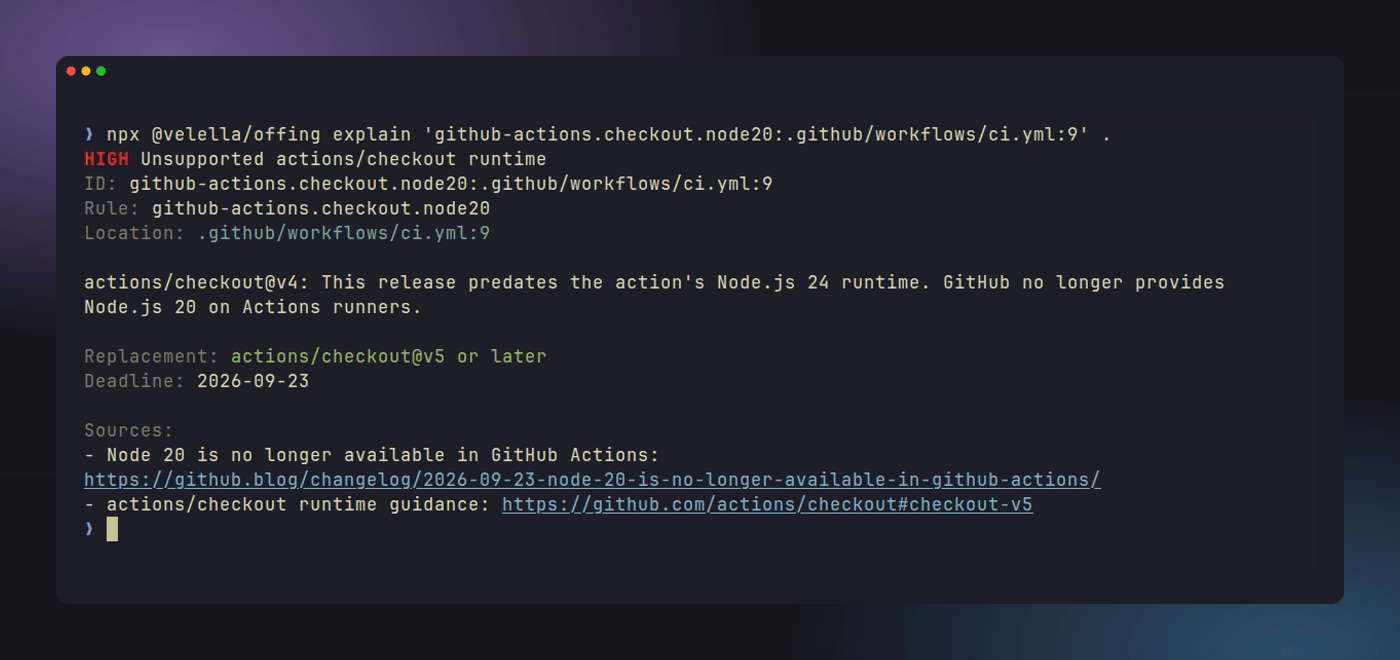 |
Adopt on day one with a baseline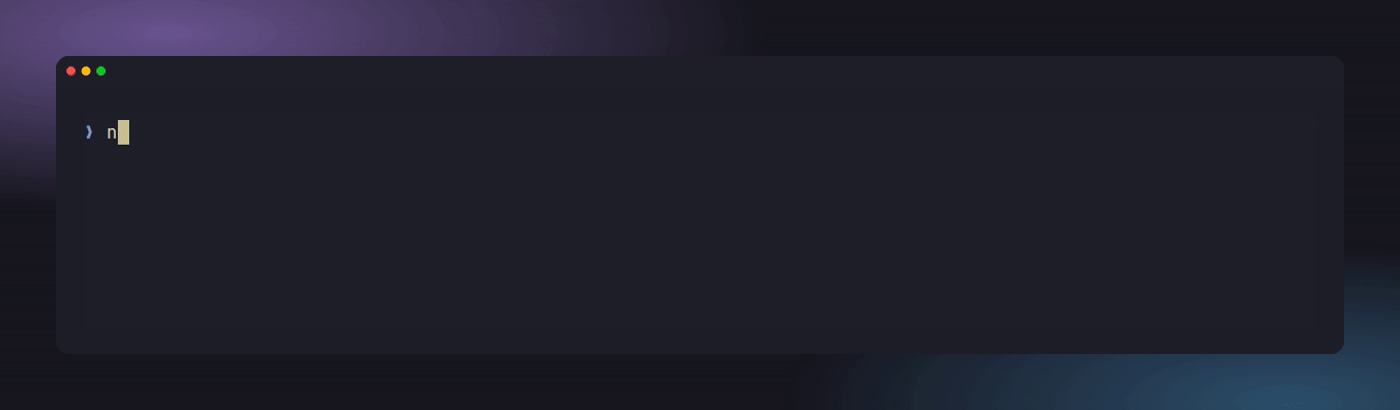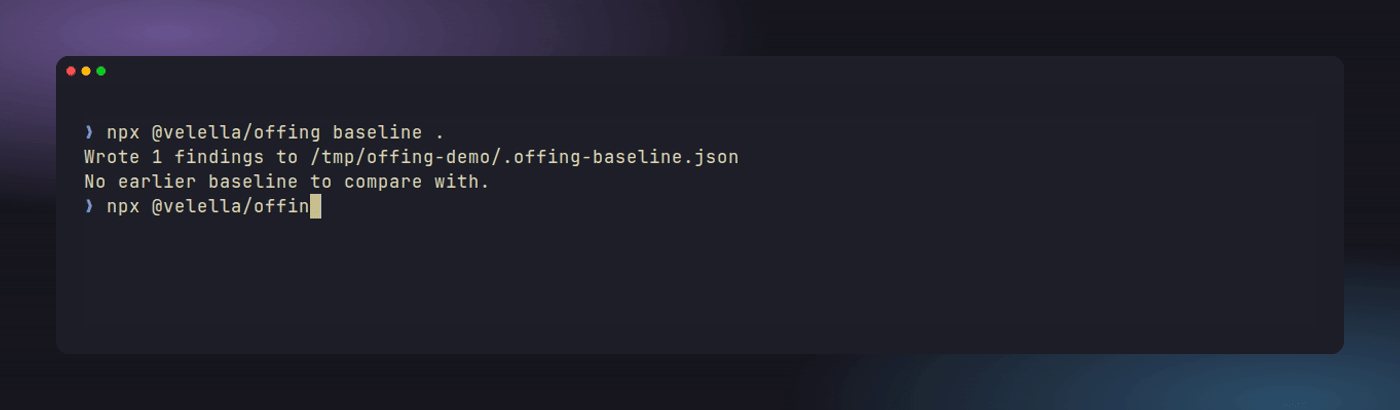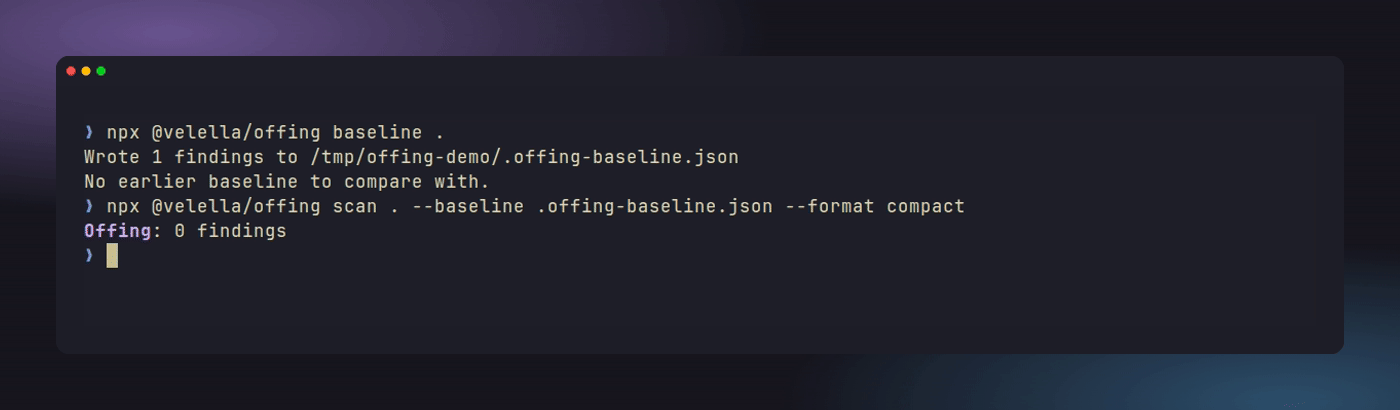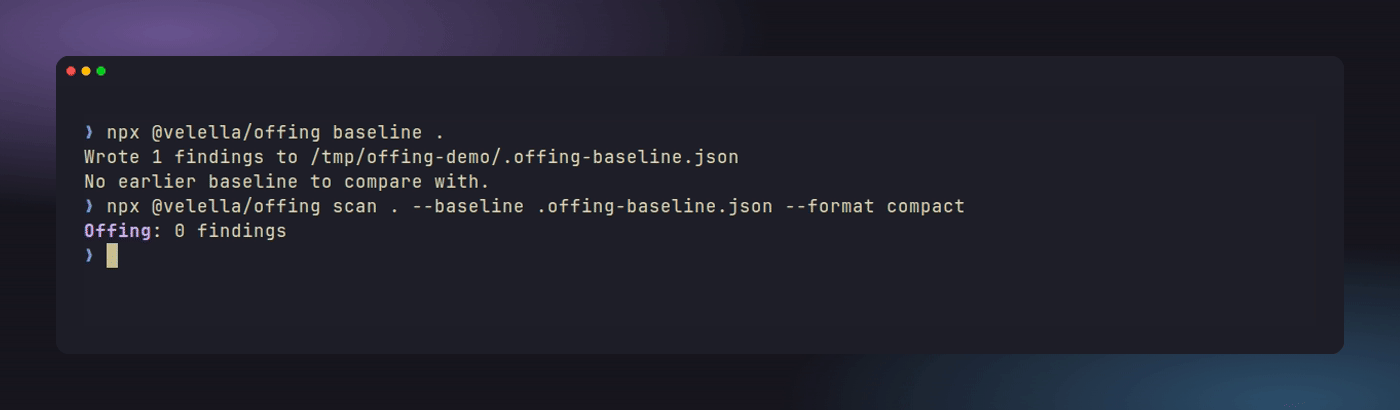 | Preview a fix as a diff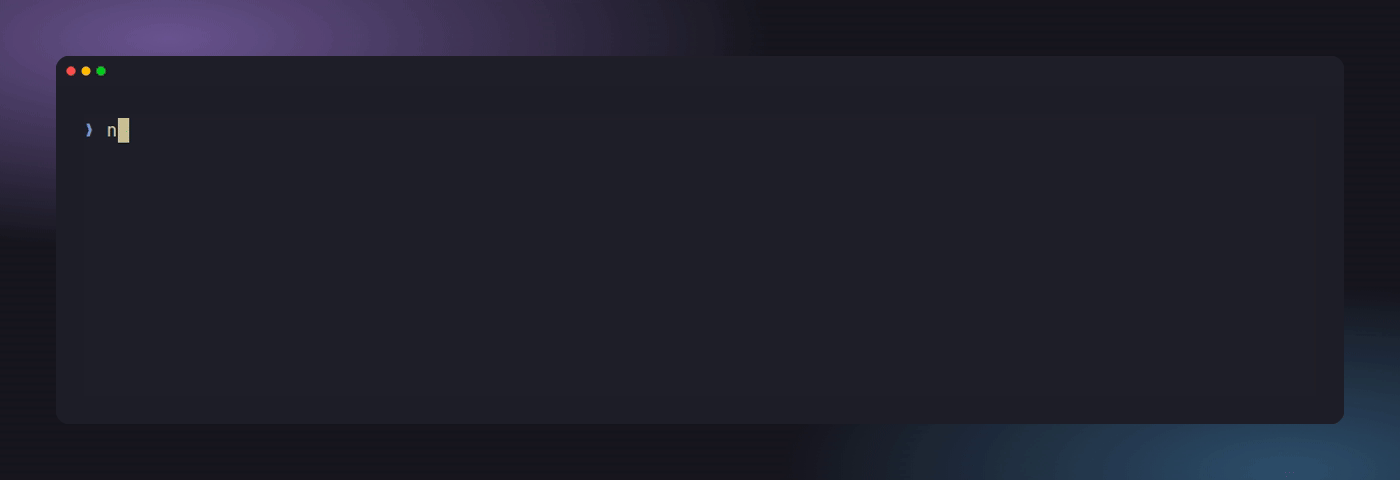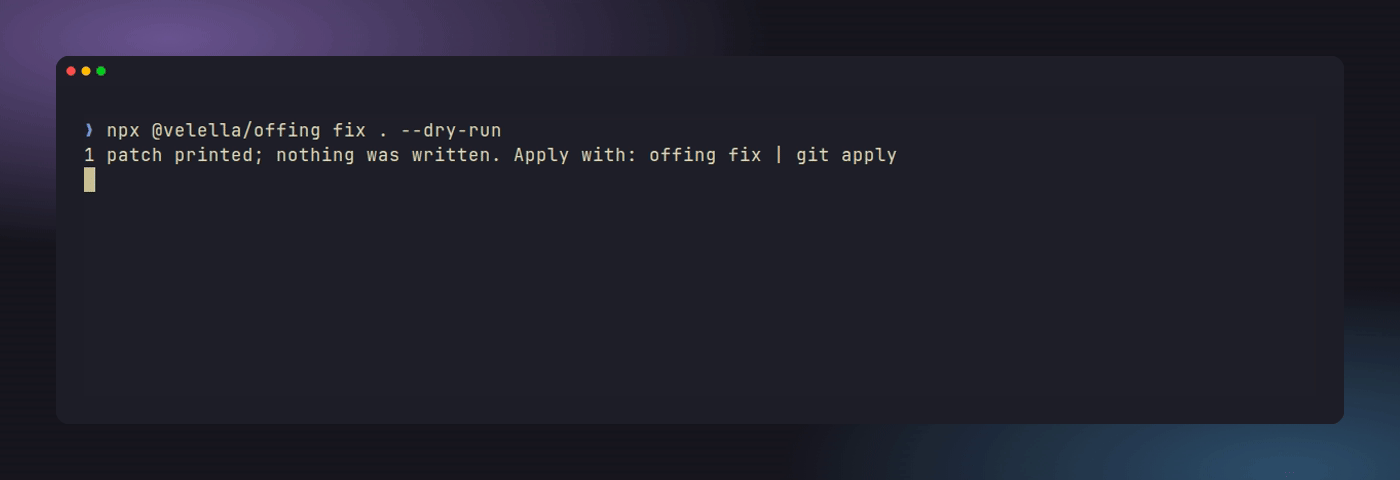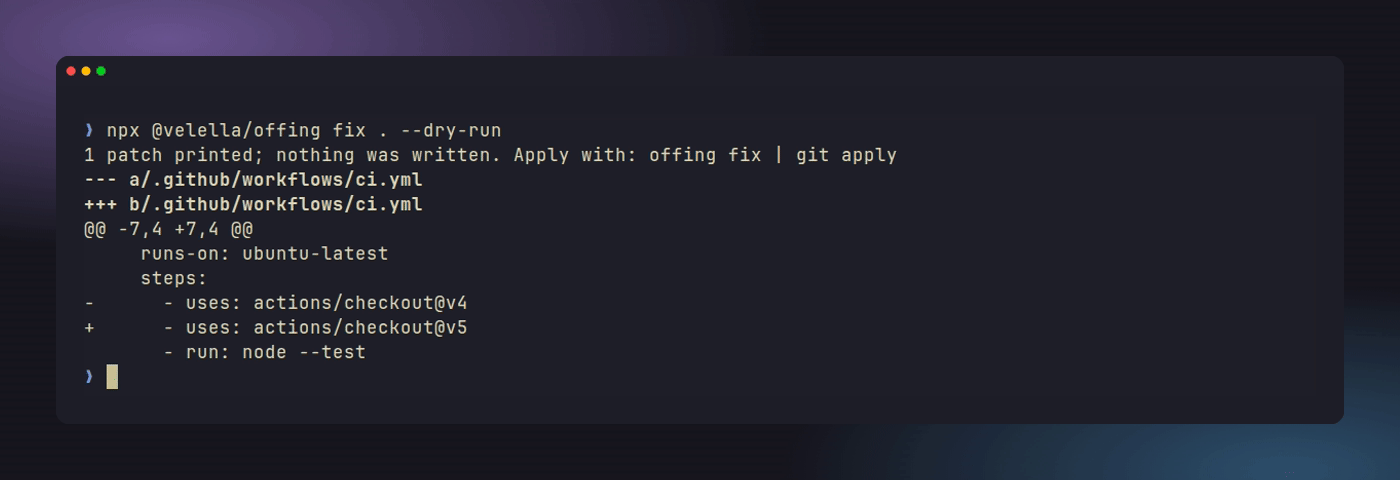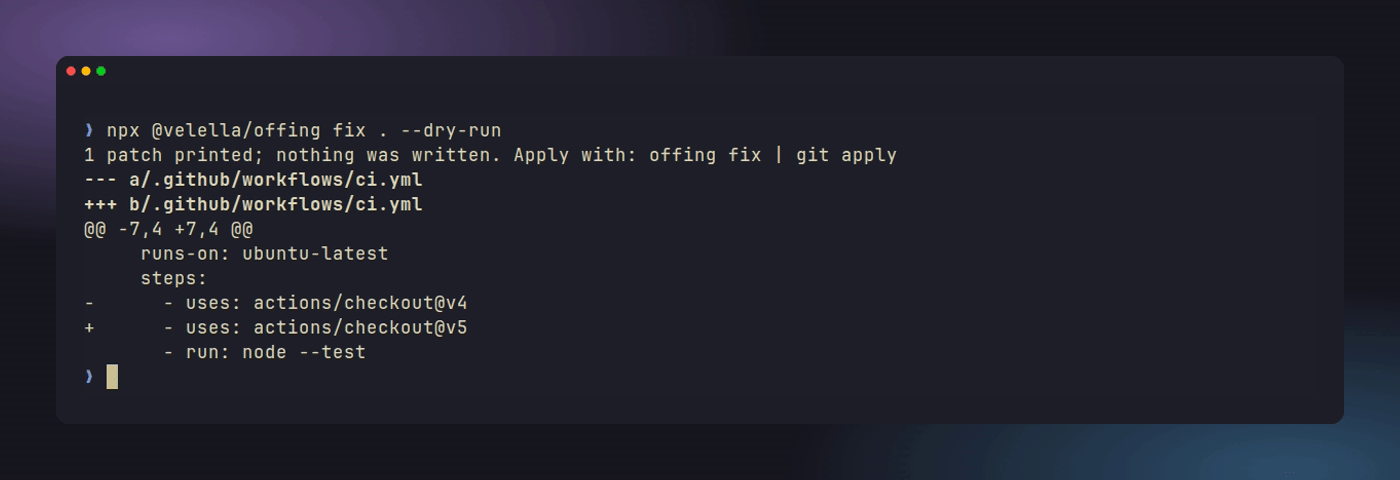 |
See what is ending next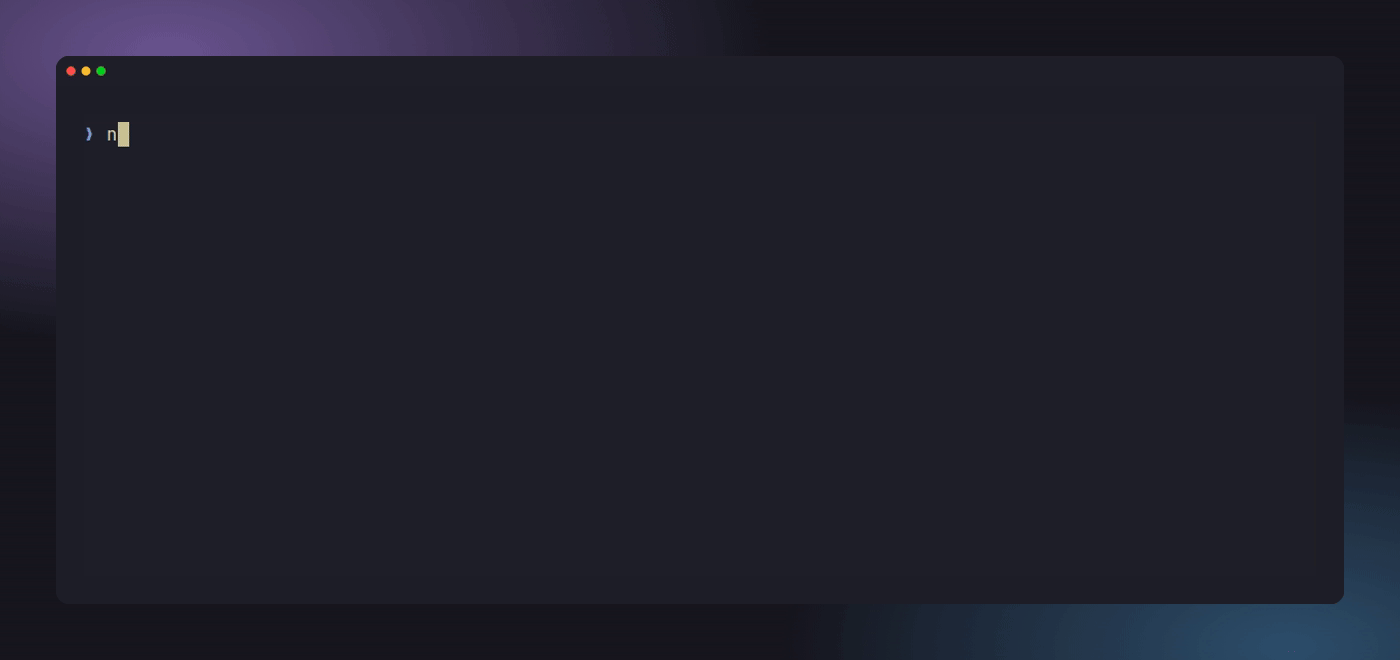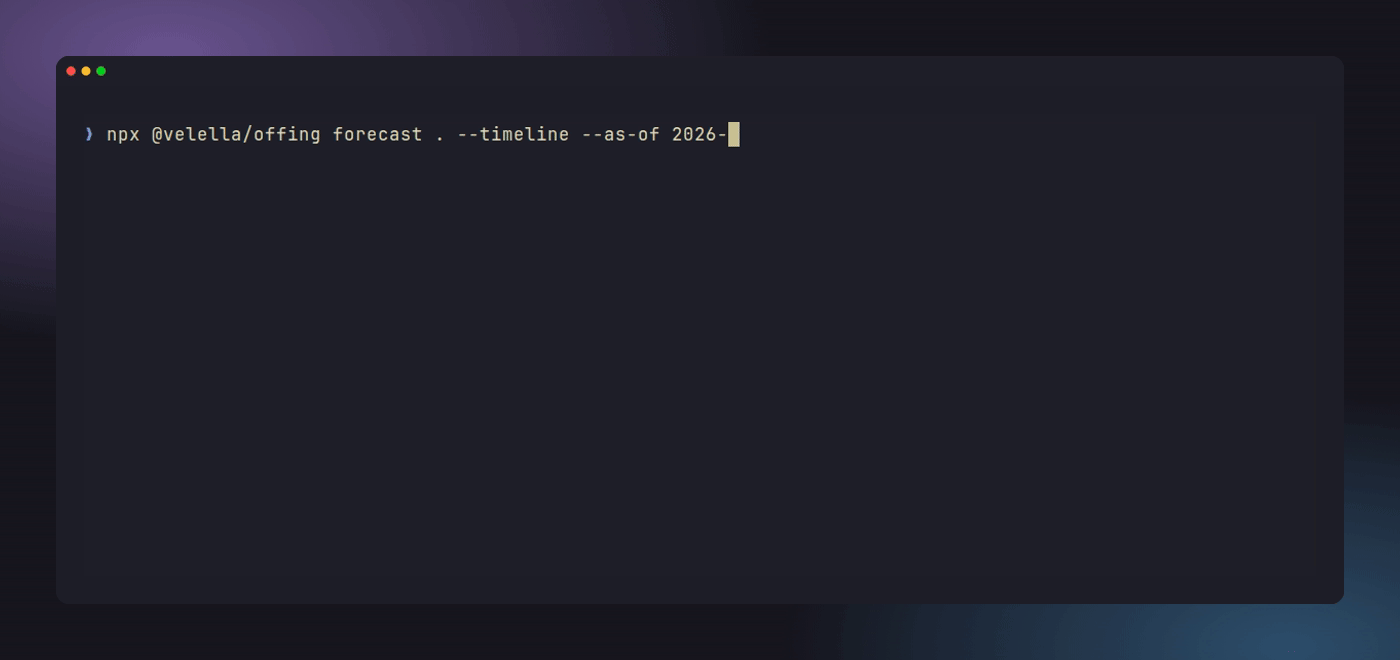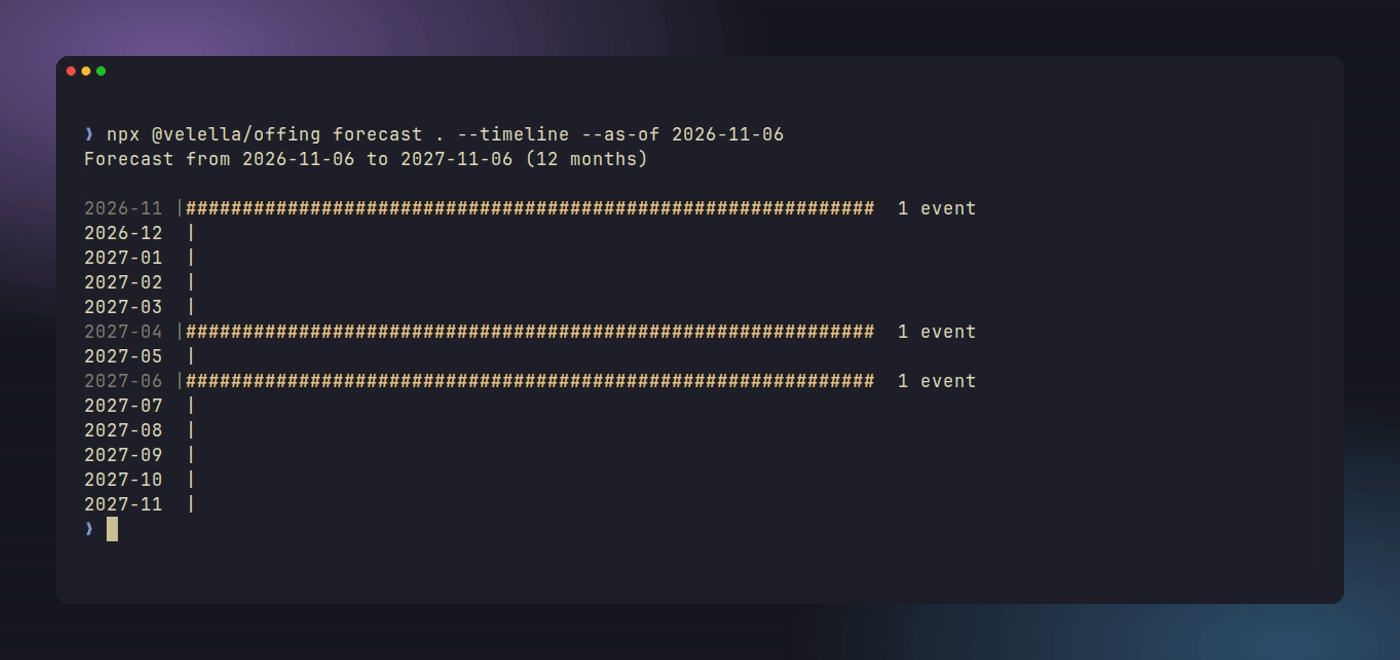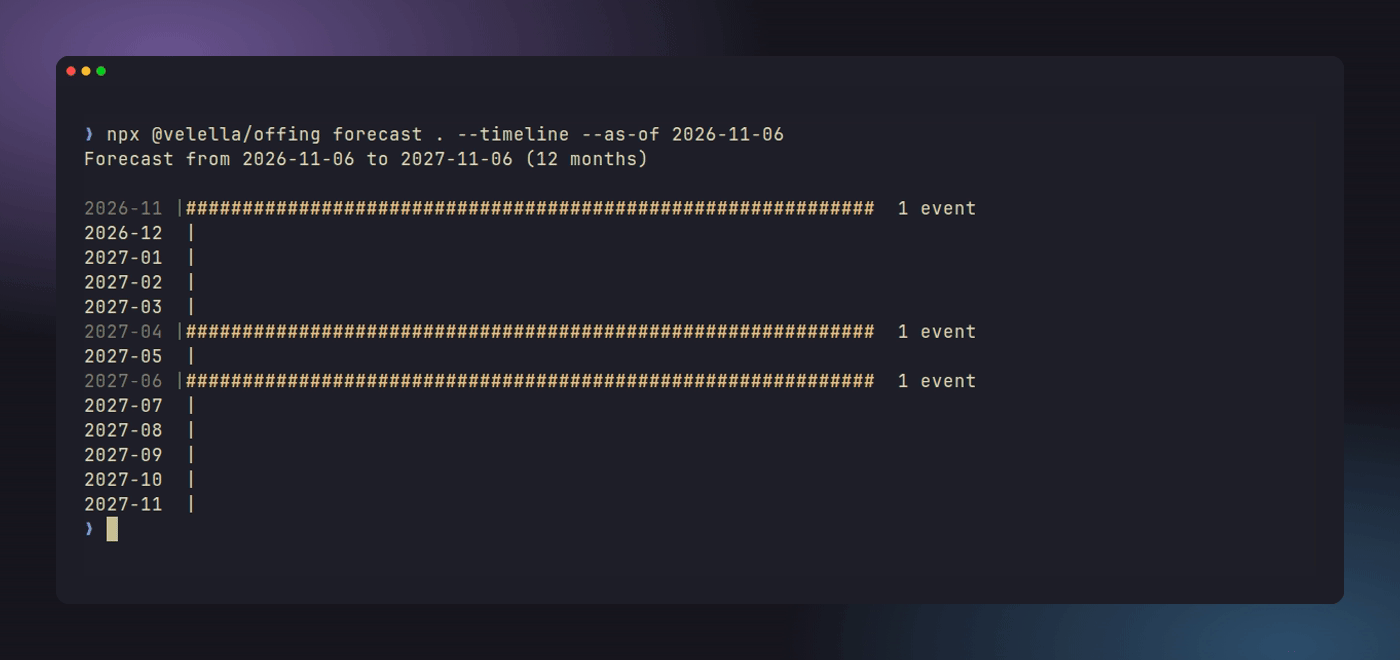 | Teach your coding agents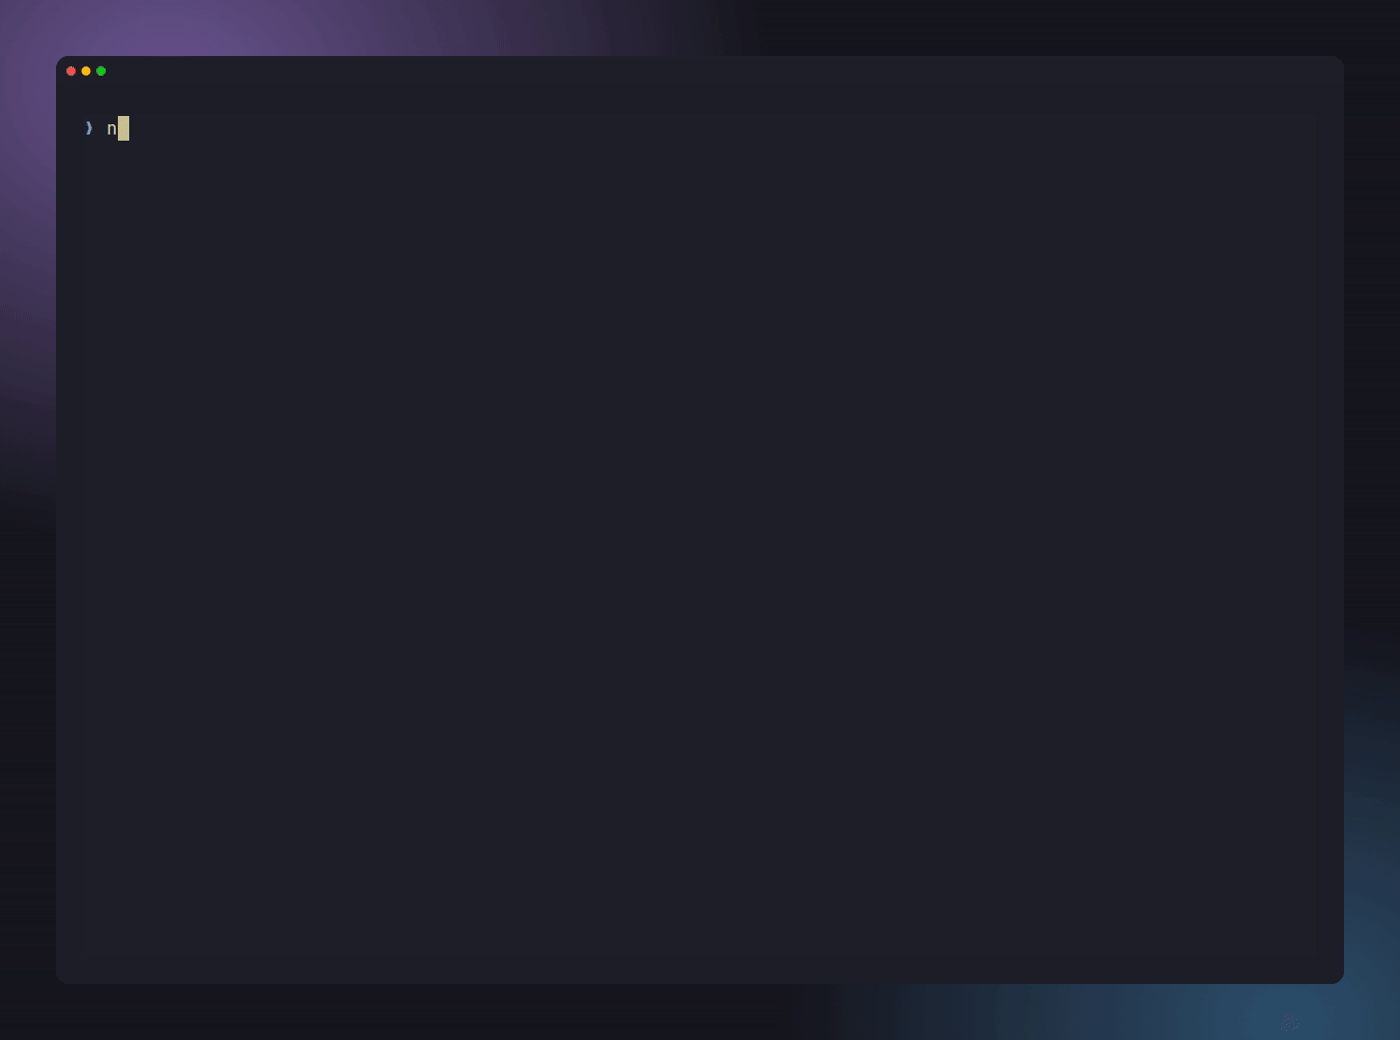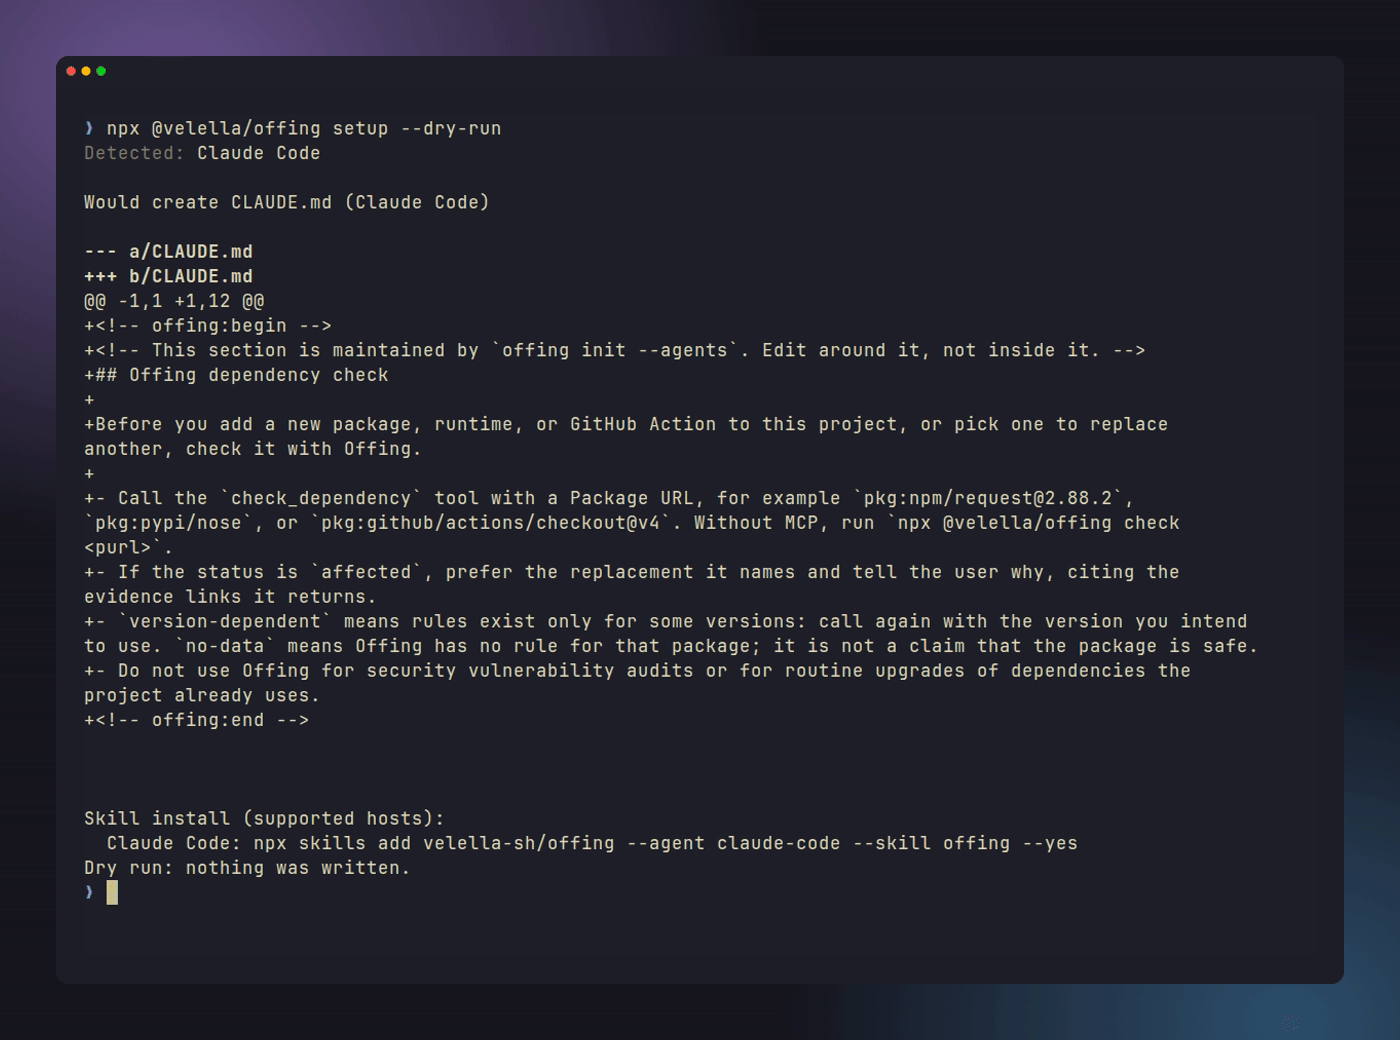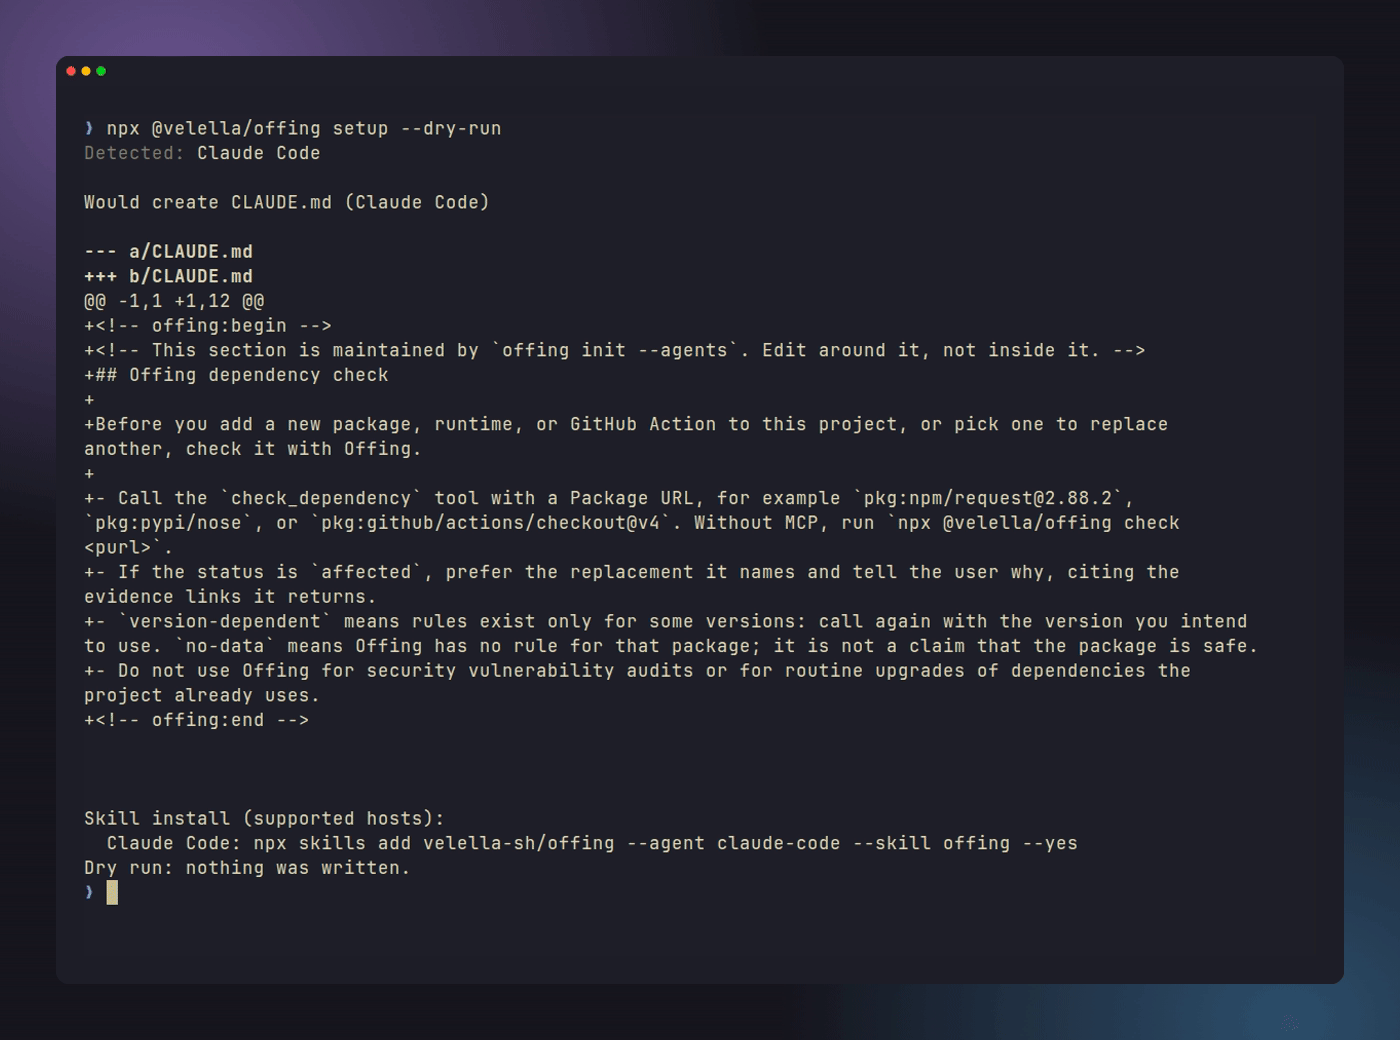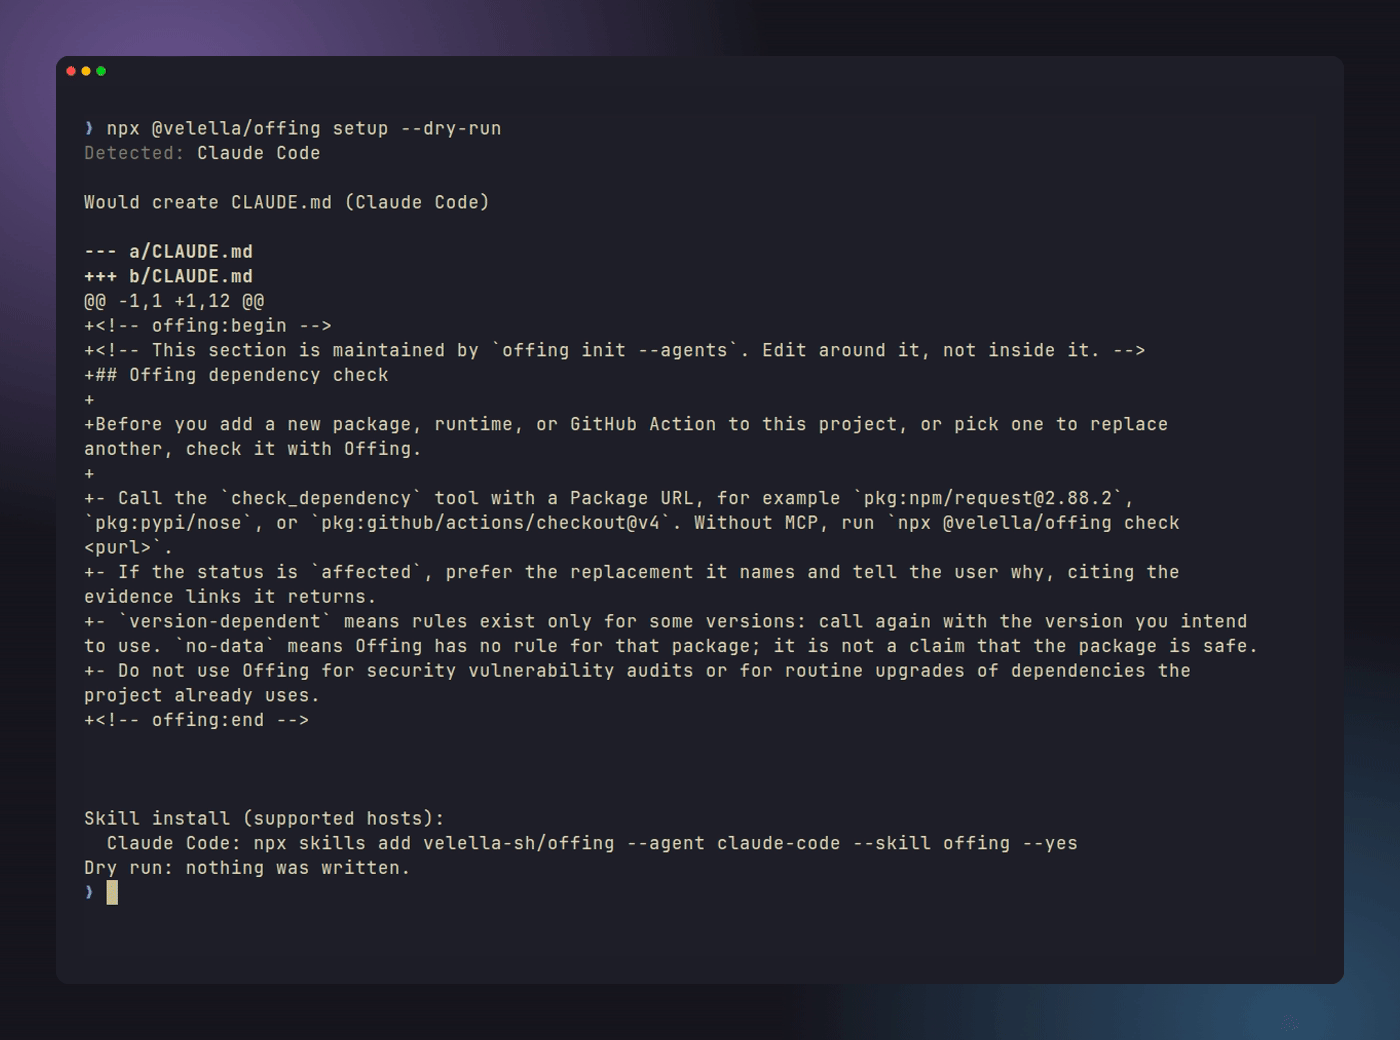 |
What it covers
Runtimes, package manifests and lockfiles, CI and infrastructure files across:
Node.js, npm, Deno and Bun · Python · Go · Rust · Java and Kotlin · .NET · Ruby · PHP · Swift · Android · Dart and Flutter · Elixir · Scala · C and C++ · GitHub Actions · CI runner images · Container base images · Kubernetes APIs · Terraform · Serverless runtimes · Database runtimes · PowerShell.
The full table, with the files read and what is reported for each, is in Ecosystem coverage. Maturity per detector is in the compatibility matrix.
For coding agents
npx skills add velella-sh/offing        # the Agent Skill, listed on skills.sh
npx @velella/offing setup               # tell each coding agent in the repo to check before adding
npx @velella/offing context '<finding-id>' . --json   # migration packet for an agent
npx --yes @velella/offing mcp           # local MCP server over stdio
Every report has a machine-readable form. The docs are also published as llms.txt and llms-full.txt. See Agent Skills and the local MCP guide.
In CI
steps:
  - uses: actions/checkout@v7
  - uses: velella-sh/offing@v0.1.1
    with:
      fail-on-severity: high
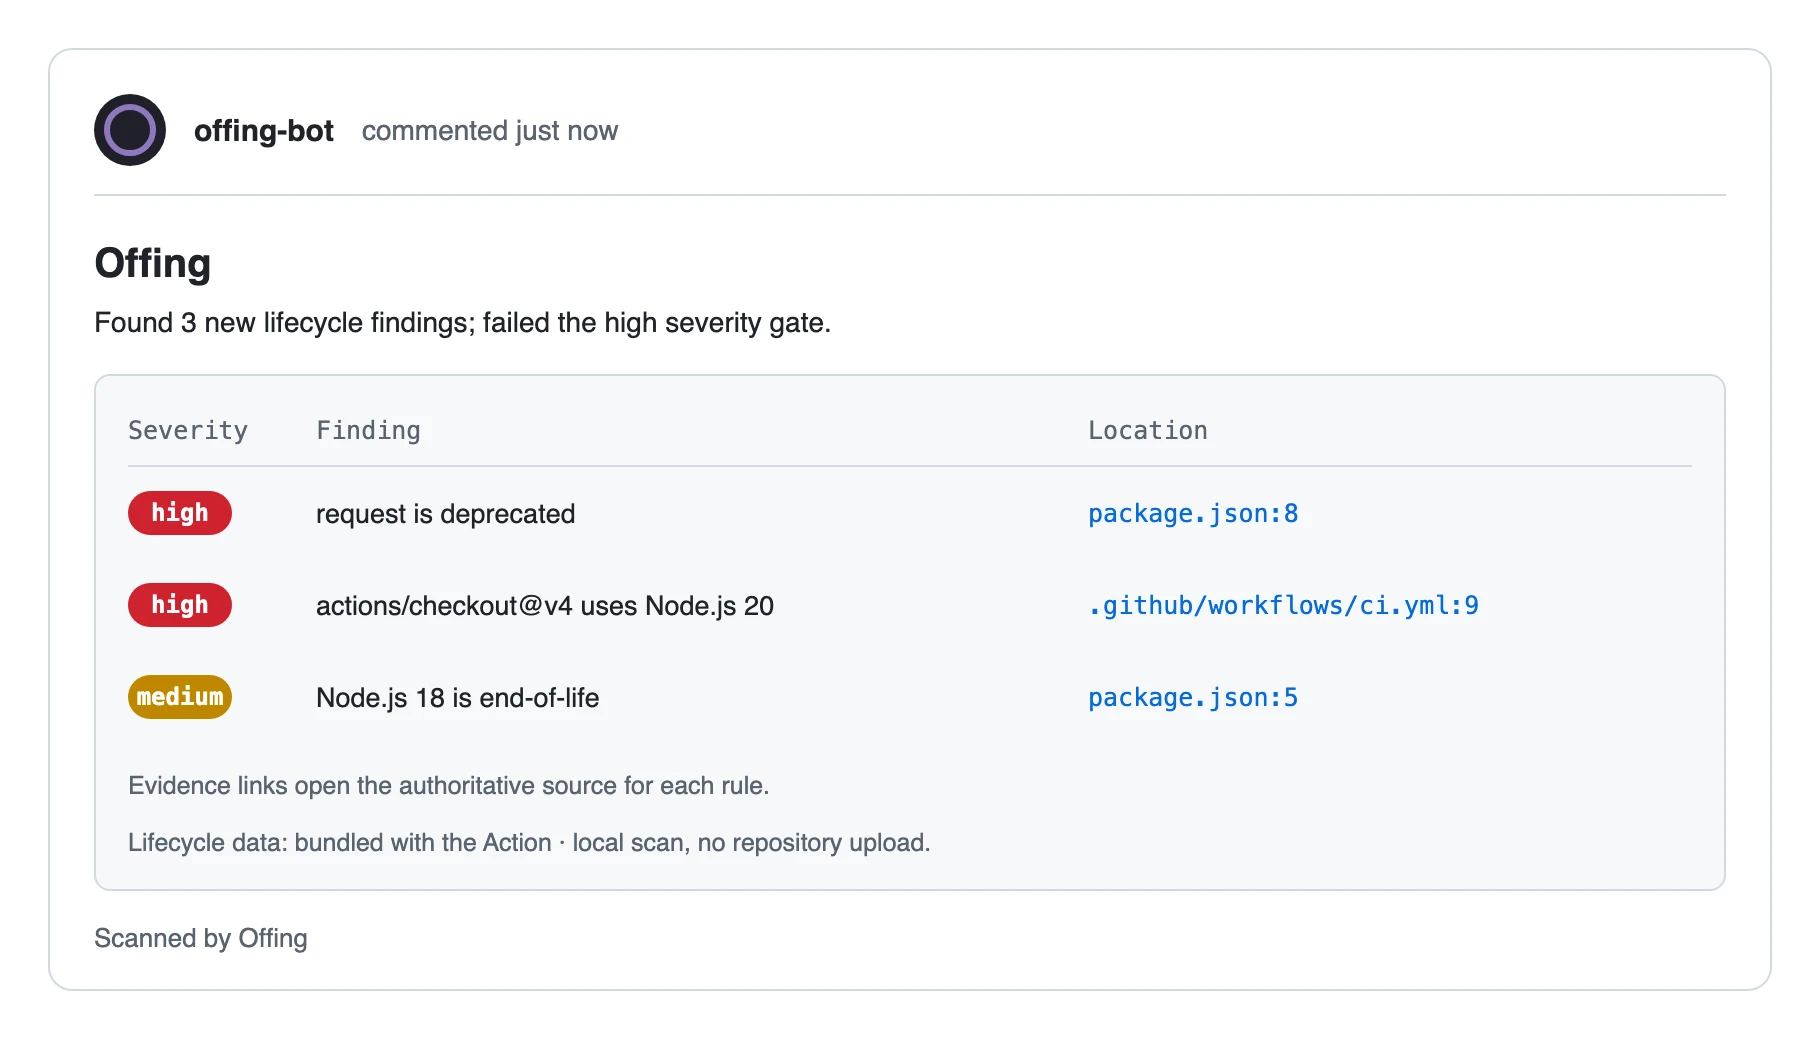
Offing annotates the pull request at the exact line, posts one summary comment with the evidence, suppresses accepted findings with a baseline, fails on the severity you choose, and uploads the complete JSON report or SARIF. Scans run on the runner, so repository contents never leave it. Pin a full commit SHA instead of a tag when you need an immutable reference. Setup, inputs, permissions and artifacts are in the GitHub Action guide.
Why not just Renovate?
Renovate, Dependabot, and endoflife.date each answer a question Offing does not, and Offing answers one none of them does: what is ending in this repository, and where is it used. Most repositories gain from running one of them with Offing, so the table states what each covers and what it does better, and links the source of every claim. Details and sources per tool are in Offing compared with other tools.
| Tool | What it covers | What it does better | Evidence |
|---|---|---|---|
| Renovate | Dependency updates across the package managers it supports, as automated pull requests | Opens the update pull requests Offing never writes, and reports npm deprecation notices for packages this registry has no rule for | Compared with Renovate; the differential report measures both directions on pinned repositories and links the evidence for every disagreement |
| Dependabot | Version updates and security updates on GitHub, each as a pull request | Version updates keep dependencies current even when nothing is vulnerable; security pull requests and alerts draw on the GitHub Advisory Database | Compared with Dependabot |
| endoflife.date | EOL dates and support lifecycles for many products, served through a public API | Product breadth beyond one reviewed rule set, and a date you can check without installing anything | Compared with endoflife.date |
| Offing | The lifecycle status of what the repository's files declare and use — end-of-life runtimes, deprecated packages, retired APIs — at file and line, offline | Reports that a version is out of support, not only that a newer one exists, and names the usage a migration has to touch | What it covers, validation, compatibility matrix |
Learn more
- Quickstart: five copy-paste steps, first scan to CI.
- Using Offing: baselines, data updates, migration packets, agent setup, the detector SDK.
- What it covers: every ecosystem, the files read, and what is reported.
- CLI reference, validation report, 90-second demo, roadmap, architecture.
- Questions and ideas: GitHub Discussions. Bugs and rule requests: issues. Security: SECURITY.md. Contributing: CONTRIBUTING.md.
License and brand
Offing source code is licensed under the Apache License 2.0. The lifecycle data it reads comes from Ebb (@velella/ebb): code under the MIT License, dataset under CC BY 4.0, attribution in ATTRIBUTION.md. The Offing name, logo, and files in brand/ are proprietary brand assets under separate brand asset terms.
@velella/offingnpm install @velella/offing